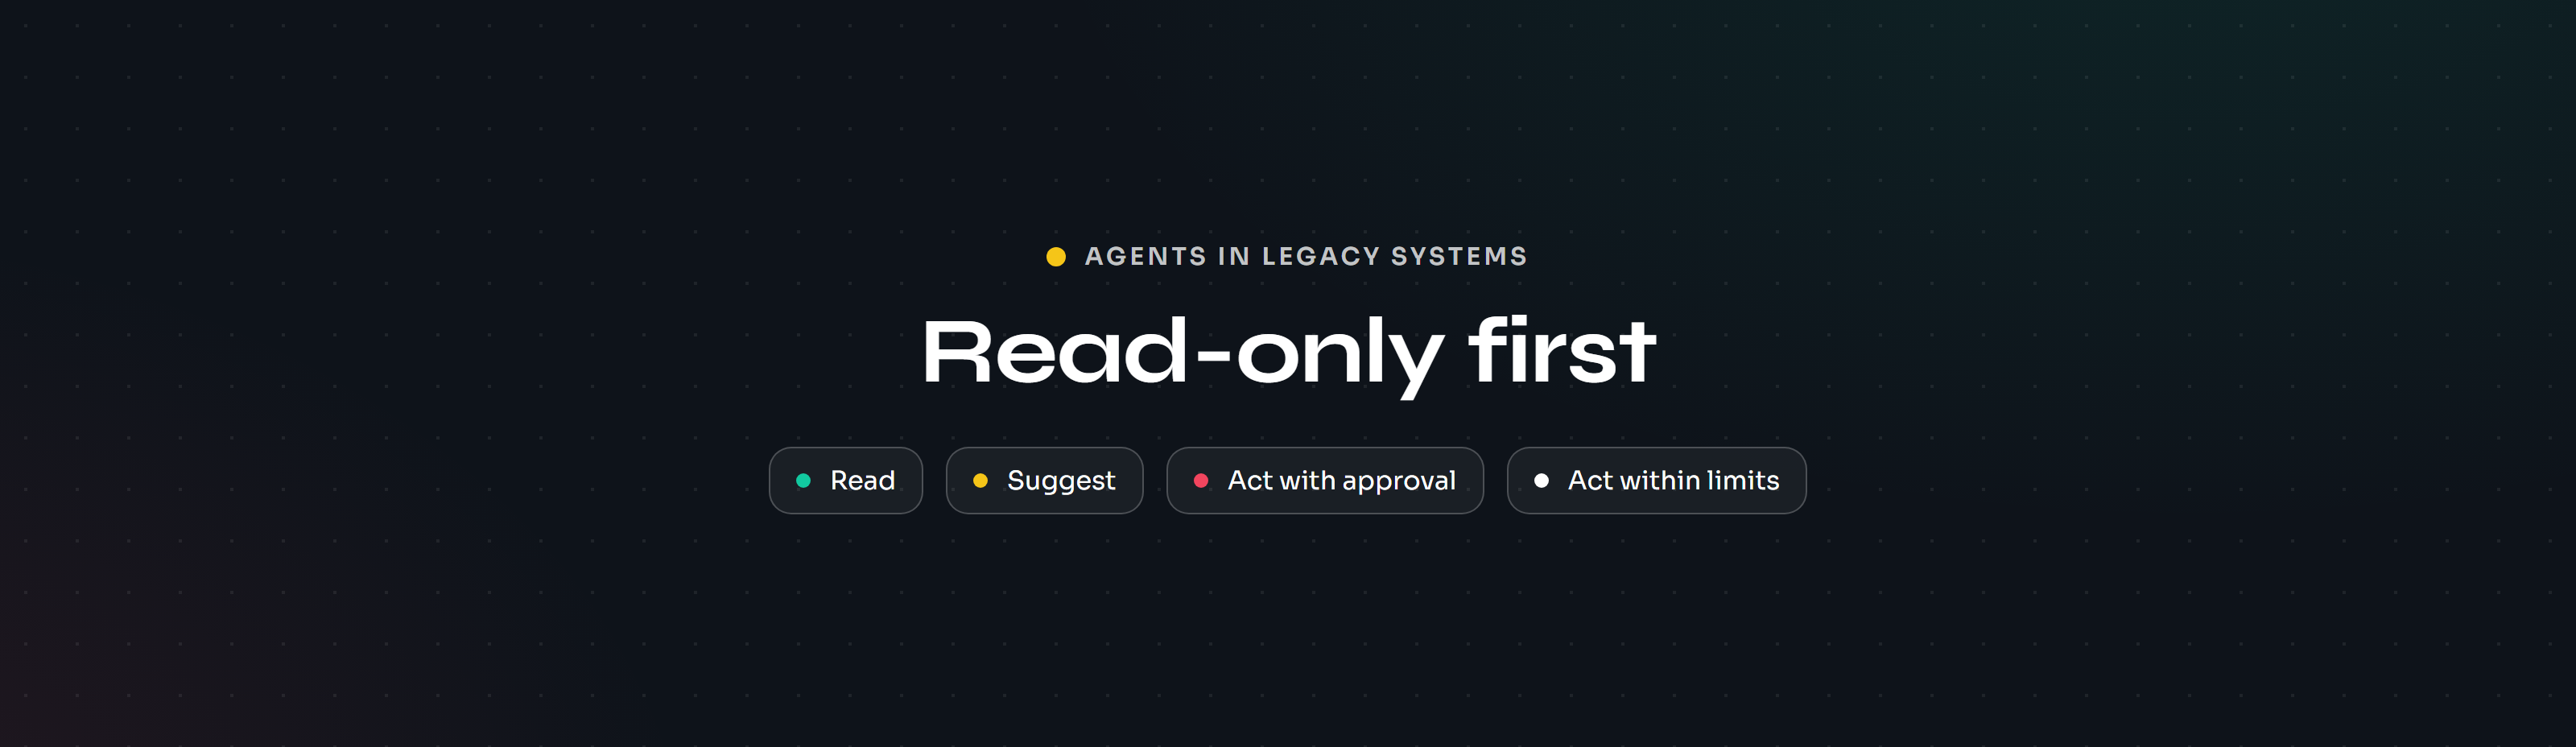
Read-Only First: How to Roll Out Agents Inside Legacy Systems Without a Security Incident
- Oct 22, 2026
AI Agents in Production | By the Zylen Solutions Team | 4-minute read
Most AI agent pilots that stall don't stall because the model is weak. They stall in the security review. Someone asks what the agent can touch, whose account it uses and how a bad change would be undone, and nobody has a good answer.
Inside legacy systems those questions are harder still. The ERP, the billing system or the old line-of-business app were built long before anyone imagined software that reads, decides and acts on its own.
Why legacy systems make this harder
- Shared accounts. Integrations often run on one service login with far more access than any single task needs.
- Coarse permissions. Many older systems can't grant "read invoices" without also granting "edit invoices".
- Writes you can't undo. No soft delete, no draft state, no clean rollback.
- Thin audit trails. Logs that can't tell you which change came from the agent and which from a person.
Giving an agent full access on day one in that environment is how security incidents happen. The alternative is to make it earn access.
The permission ladder
We roll agents out in four stages. Each one adds a little more trust, and the agent only moves up when it has proved itself at the current one.
- Read. The agent reads data and writes nothing. It runs in shadow mode alongside the team, and its answers are compared with what people actually did.
- Suggest. The agent drafts the action, such as matching an invoice to a purchase order. A person reviews it and carries it out.
- Act with approval. The agent can write, but every write goes through an approval queue first.
- Act within limits. The agent acts on its own, but only for small, reversible actions inside limits you set, and every action is logged.
Many workflows never need to go past stage 2 or 3, and that is fine. The goal is the least access that still does the job.
Shadow mode in practice
Stage 1 is where most of the learning happens. Give the agent read-only credentials, or point it at a replica of the data. Let it work through real cases next to your team for a few weeks. Block and log any write it attempts. By the end you know how often it agrees with your team, where it goes wrong, and whether it ever tried to reach for something it shouldn't.
When to move up a rung
Promotion should be a decision, not a drift. We move an agent up only when four things are true:
- Accuracy holds at the level you agreed, over weeks rather than one good demo.
- The logs are clean: no access outside its scope, and every action traced to the agent.
- Rollback is tested: you have reversed a change on purpose and it worked.
- An owner signs off: a named person in the business approves the next stage.
Guardrails that stay on
Some controls apply at every stage, from the first read onward:
- Short-lived, task-scoped secrets that never appear in a prompt.
- Only the tools the current stage needs.
- Network egress limited to what you allow.
- A full audit log of every read, draft and write.
- Untrusted text treated as data rather than instructions.
- A kill switch that drops the agent back to read-only in one step.
Where to start
Pick one workflow, give the agent read-only access, and run it in shadow mode for two weeks. You will learn more about whether it is ready than any demo can tell you, and you will have the evidence a security reviewer needs.
How we approach it at Zylen
Zylen is an AI optimization partner. We work inside the AI systems companies already run. Our ten-day AI Optimization Audit assesses your AI paths against the OWASP GenAI LLM Top 10 2026 and hands you a versioned findings register, so you know what is safe to switch on first. It is an engineering assessment, not a penetration test or certification.
Earn write access, don't grant it: start the AI Optimization Audit
About Zylen
Zylen is an engineering firm working on AI cost, security and sovereignty. We meter what inference actually costs, put guardrails in front of AI systems, and run open models inside our customers' own infrastructure.
Recent Posts
Read-Only First: How to Roll Out Agents Inside Legacy Systems Without a Security Incident
Build vs Buy vs Embed: How to Pick the First AI Use Case Inside a Real Company
From Advice to Production: Why Forward-Deployed Engineering Is Replacing Consulting
Why Offline Evals Lie: Building Eval Users That Behave Like Real Ones
Categories
- AI Engineering
- AI Cost Optimization
- Company News
- Healthcare IT
Newsletter
Contact us
Have a project in mind? We would love to hear from you.
Send